🔍 Read the full analysis: A16z’s US Infrastructure Plan: Fast AI Defense, Drills, And Gaps on ThorstenMeyerAI.com

Get smart everyday buys delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
TL;DR
Andreessen Horowitz published a proposal on November 12 for protecting key U.S. infrastructure as AI speeds up cyberattacks and defense. It calls for sector targets, 72-hour manual-operation drills and monthly reporting, but it is not policy and does not specify costs.
Venture firm Andreessen Horowitz (a16z) published a proposed cyber defense plan on November 12 that would focus federal and industry efforts on a few hundred operators and shared vendors across five critical infrastructure sectors. Written by a16z General Partner Anne Neuberger, the proposal calls for measurable security targets and regular reporting as AI accelerates the pace of cyber threats; it is not current U.S. policy.
The plan covers power, banking and payments, water, communications, and hospitals. Rather than attempting to secure every system at once, it argues that the greatest national risk is concentrated among operators and vendors whose disruption could have cascading effects. Examples listed in the proposal include major power substations, payment systems, large-city water utilities, core telecommunications and 911 systems, regional trauma centers, and health-record vendors.
For each sector, the plan proposes that participating chief executives sign targets covering zero internet-exposed control systems, passing drills to operate manually for 72 hours, and containing critical vulnerabilities—through a patch or a compensating control—within a set period. The highest-priority targets should be contained within six months, according to the source account. Industry Information Sharing and Analysis Centers, or ISACs, would coordinate work and submit anonymized sector metrics each month.
The proposed governance structure assigns the White House’s Super Intelligence Force responsibility for setting national targets, convening monthly CEO reviews, and addressing policy or funding barriers. A CEO council would answer for sector results, while ISACs would coordinate technical work with companies and vendors. The plan also proposes legal protections for participating companies, including long-term reauthorization of the Cybersecurity Information Sharing Act of 2015 and a possible safe harbor for firms that meet outcome-based targets.
The a16z plan in motion · schematic
From a CEO pledge to the President’s table
How the proposed cyber defense plan for power, banks, water, telecom and hospitals is meant to work, step by step. It is a proposal, not policy.
The chain, step by step
Each circle is one step of the plan; the ring marks the step being explained.
What happens at each step
- 1CEO pledgeA CEO council, with 2–3 CEOs per sector, commits each sector to national targets set by the White House’s SI Force.
- 2Three targets, signedZero internet-exposed control systems72-hour manual-operation drills passedCritical flaws contained within a set time
- 3DrillsTop targets prove they can run without IT for 72 hours. A joint cross-sector drill, modeled on GridEx, within 3-6 months.
- 4Monthly scorecardsSector ISACs report anonymized metrics to the SI Force. A sector behind target triggers a CEO-level review.
- 5President councilThe CEO council is publicly accountable for results and meets the President every six months.
Source: a16z, “Super Intelligence-Era Critical Infrastructure Cyber Defense Plan”, November 12, 2026, incl. its governance table (“For illustrative purposes only”). The chain is a schematic of the proposal, not an existing program.
Graphic: Powered by Thorsten Meyer AI
Targets for High-Impact Systems
The proposal’s focus is on reducing the chance that a cyber incident affecting one operator or vendor will disrupt services across a wider area. Power, payments, water, communications and hospitals underpin everyday services, and the plan argues that protecting a limited set of connected organizations could have more immediate value than trying to cover every system equally.
Its targets would also shift attention from sharing threat alerts to demonstrating operational readiness. A 72-hour manual-operation drill, for example, would test whether a service can continue during a serious technology disruption. Monthly scorecards and CEO-level reviews could make senior leaders more directly responsible for progress. Those measures remain proposals, however; the source does not establish that agencies or companies have adopted them.
The plan frames AI as both a risk and a possible defensive tool. It says AI can help identify exposed systems, prioritize vulnerabilities and produce fixes, including workarounds for equipment that cannot be patched. Whether those tools can be deployed quickly and safely at the scale required is not established in the proposal.
Products Worth Considering

Dell UltraSharp U3225QE 31.5-Inch 4K UHD 120Hz IPS Black Thunderbolt Hub Monitor
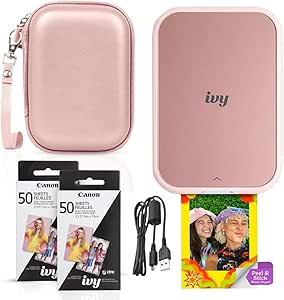
Canon IVY 2 Mini Photo Printer Bundle, Blush Pink

HP Sprocket Studio Plus Wireless 4×6 Photo Printer
As an affiliate, we earn on qualifying purchases.
From Government Cyber Work to a16z
Neuberger previously worked on infrastructure security in the U.S. government, including at the National Security Agency and as deputy national security adviser for cyber and emerging technology, according to the source material. She is now a general partner at a16z and authored the plan. That background informs the proposal, but it does not give the document official government status.
The proposal is addressed to the White House’s Super Intelligence Force. The source material says President Donald Trump announced the task force on October 4, 2026, and named National Intelligence Director Jay Clayton to lead it, citing NBC News. a16z describes its suggested model as accountable to that force, with infrastructure-sector CEOs leading implementation. Its governance table is labeled “For illustrative purposes only.”
The source account also identifies a potential conflict-of-interest concern: a16z invests in frontier AI laboratories and security companies, categories that could have a role in the proposed effort. That is relevant context for evaluating the firm’s recommendations, but the material does not show that any particular investment would receive a contract or formal position.
“AI is shrinking the time between when a weakness is found and when it is exploited. Defenders who still work at human speed will lose that race.”
— Anne Neuberger, a16z general partner, as quoted in the plan
The proposal does not state how much the plan would cost, how that spending would be divided, or how companies would be selected for its priority list. It also does not set out a complete schedule for every sector target. The source account says the top targets should be contained within six months, but does not explain how that deadline would be measured or enforced.
It remains unclear whether the White House’s Super Intelligence Force will take up the proposal, whether Congress would reauthorize the 2015 information-sharing law, or what any safe harbor would cover. The plan describes public-company board attestations and regulator acceptance in place of duplicate audits, but the source material does not establish that regulators have agreed to that approach.
Participation by smaller operators is another open issue. The plan suggests that larger utilities, health systems, banks and carriers support smaller organizations, including rural providers. It does not specify the funding, obligations or liability rules for those arrangements. Nor does the source demonstrate how quickly AI tools could identify and remediate vulnerabilities across older or hard-to-patch equipment.
Whether Washington Adopts the Proposal
The immediate next step is for the White House and relevant agencies to decide whether to consider the plan and whether the proposed force, CEO council and ISAC reporting structure fit existing responsibilities. The proposal names the Department of Energy, Treasury, the Environmental Protection Agency, the Federal Communications Commission and the Department of Health and Human Services as sector agencies, but does not say they have endorsed the framework.
Any move toward implementation would require further decisions on funding, deadlines, company participation, legal protections and oversight. Congress would also have to act on any reauthorization of the Cybersecurity Information Sharing Act. Until those steps occur, the targets and scorecards remain recommendations, not requirements for infrastructure operators.
Key Questions
What did a16z propose?
a16z proposed a White House-led effort to improve cybersecurity across power, banking and payments, water, communications and hospitals, with measurable targets and monthly reporting.
Is the plan already U.S. policy?
No. It is a proposal published by a16z. The source material does not say the White House or agencies have adopted it.
What targets does the proposal set out?
It calls for zero internet-exposed control systems, successful 72-hour manual-operation drills, and critical vulnerabilities contained within set periods. The plan says top targets should be contained within six months.
Who would oversee the proposed effort?
The plan assigns target-setting and monthly reviews to the White House’s Super Intelligence Force. A CEO council would answer for sector results, while ISACs would coordinate work and report anonymized metrics.
What is still unknown?
The proposal does not specify its total cost, confirm company participation, or establish that Congress and regulators will approve its proposed legal protections and reporting arrangements.
Source: ThorstenMeyerAI.com