🔍 Read the full analysis: Why Google Took Down A 1.3-Million-Device TV Box Botnet on ThorstenMeyerAI.com

Get smart everyday buys delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
TL;DR
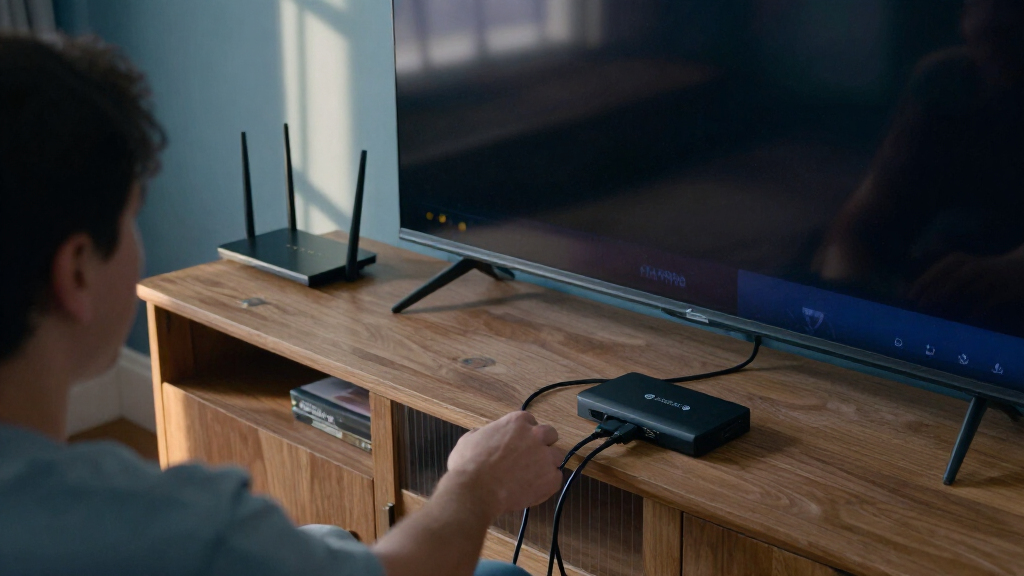
Google and industry partners say they disrupted the XCPE botnet in late October, cutting off control servers used to manage more than 1.3 million set-top boxes. Google attributes the firmware backdoor to device maker Videostrong; the company has not responded to media requests, and the backdoor may remain on affected devices after the takedown.
Google says it and its partners disrupted the XCPE botnet in late October, cutting off control servers used to manage more than 1.3 million Android set-top boxes. The company says the malware was embedded in device firmware and attributes its development and operation to manufacturer Videostrong Technology Co., a claim that makes the incident a supply-chain security problem, not simply a case of users downloading a malicious app.
Google’s Threat Intelligence Group (GTIG) published its account on November 2, saying the operation involved Japan’s National Police Agency and security firms Lumen, HUMAN Security, Plume, Synthient and TrendAI. The partners took legal action to disrupt domains and servers that Google says Videostrong used to control the botnet and distribute malware. Google also said it acted against control servers for more than a dozen malware families that had been added to infected boxes.
The number depends on how it is described. Google reported more than 1.3 million set-top boxes. TrendAI separately counted 1,472,554 infected devices between June 3 and October 1, 2026, describing that figure as a lower bound. The count is a measurement over that stated period, not a claim that every device remained infected simultaneously.
Google says most of the boxes were used as residential proxies, routing other people’s internet traffic through household connections, and for ad fraud. GTIG also reported capabilities to take screenshots, inject keystrokes, collect account and device information, and open remote shells. These are capabilities described by Google; the published source material does not establish how often each was used or what specific victims experienced.
Infographic 01 · XCPE in numbers
A botnet that shipped from the factory
Google says the device maker Videostrong built the backdoor into its own firmware and sold access. That is Google’s assessment; Videostrong did not respond to the press.
set-top boxes in the XCPE botnet, the joint figure of Google and its partners. Taken down in late October 2026.
- 1,472,554 infected devices in TrendAI’s own telemetry, 3 Jun to 1 Oct 2026, a lower bound.
- Partner counts differ by snapshot and view, so the joint figure is “more than 1.3 million”.
- 10M+ more devices lost their malware’s control servers: Google’s estimate, not a count.
How one box earns money for criminals
- Built inA system app sits in the firmware and reinstalls itself after a reboot
- Phones homeOn start it fetches settings and keeps a line open to a control server
- Sold onAccess is sold to partners, who push their own modules
- Cashed inResidential proxy, hidden ad views, more backdoors
Your home internet address is the product. Strangers rent it, and their traffic looks as if it came from your living room.
Sources: Google Threat Intelligence Group, 2 Nov 2026 · TrendAI, 2 Nov 2026. Simplified for readers; no indicators or technical details reproduced.
Powered by Thorsten Meyer AI
Why Infected Boxes Matter
Residential proxy traffic can make activity from a criminal operator appear to come from an ordinary household or office. That can expose the owner of an infected connection to unwanted traffic and make it harder for services to distinguish legitimate users from automated activity. Ad fraud can also distort advertising systems and divert revenue, although the available report does not quantify losses linked to XCPE.
The case also tests the security assurances attached to certified devices. Google says some infected boxes carried its certification, and that Videostrong used obfuscation to load malicious code after a device’s first boot, bypassing checks. Google says it has banned Videostrong from building certified Android devices or supplying software to certified vendors, including future subsidiaries or affiliates, and has tightened firmware-integrity reviews.
Google estimates that action against control servers for the additional malware families could cut off access to at least 10 million more compromised devices. That is Google’s estimate, not a verified device count; the source account says those devices were reached through other channels and were not all necessarily Android devices. The distinction matters: the XCPE total and the wider projected effect describe different groups.
Products Worth Considering

Apple iMac 24-inch All-in-One Desktop Computer with M6 Chip, Blue

Apple Mac mini Desktop Computer with M6 Chip (2026)

Apple iMac Pro (27-inch Retina 5K Display, 3.2GHz 8-core Intel Xeon W, 32GB RAM, 1TB SSD) – Space Gray
As an affiliate, we earn on qualifying purchases.
How the Firmware Backdoor Worked
GTIG says the backdoor was a system application embedded in firmware, identified in some versions as x.cpe and in others as com.oemservice. It had system-level privileges and, according to Google, could reinstall itself from a protected partition after a reboot if removed. That means uninstalling an associated app would not necessarily remove the underlying access.
After startup, the software contacted a control server, received settings and maintained a connection that allowed operators to issue commands. Google says the malware could disable Google Play Protect checks before silently installing other applications. Since at least late 2024, GTIG observed a design with separate components for server communications, loading code and running partner-supplied modules. In August 2026, Google observed new droppers disguised as Android system apps replacing the loader.
Google’s report characterizes Videostrong as an Android original equipment and design manufacturer, meaning it produced devices for its own brands and for other companies. It says the backdoor and botnet were intentionally developed and operated for financial gain, with access sold to criminal partners. Videostrong did not respond to requests for comment from The Record and heise, according to the supplied source account.
“The backdoor and the botnet were intentionally developed, deployed, and operated for financial gain by Videostrong Technology Co.”
— Google Threat Intelligence Group
What the Takedown Leaves Behind
Disrupting control servers can stop operators from reaching affected devices through that infrastructure, but it does not by itself remove firmware already installed. The source account says the backdoor can return after a reboot from a protected partition, and Google has not described a universal cleanup method. The current status of each infected box, and whether operators retain any other means of control, is not established in the material provided.
Other details remain unsettled. The supplied account says Google did not publish the court filing and that no public case record was found, so the court, case number and precise legal process are not available here. Videostrong’s response is also unknown. Google has not provided a device-by-device list in the source material, nor a breakdown of confirmed harms, financial losses or the number of boxes still online.
Device Checks and Security Changes
Google says it has changed its review process for certified Android TV firmware and barred Videostrong from the certified-device program. The source material does not specify a public timetable for those checks or describe whether Google will issue updates for affected models. Owners should check a device’s Play Protect certification, be cautious about no-name or “unlocked” boxes, and avoid treating an app uninstall as proof that firmware-level malware is gone.
For a box suspected of infection, the source account advises unplugging or replacing it and placing TV boxes on a separate guest network. Businesses should account for home and office connected devices in their security planning rather than relying on a device’s IP address or reputation alone. Whether further law-enforcement or industry actions will identify affected models or produce remediation guidance remains to be seen.
Key Questions
What happened to the XCPE botnet?
Google says it and partners disrupted the botnet’s control infrastructure in late October 2026. The operation targeted servers and domains used to manage infected set-top boxes and distribute malware.
How many devices were affected?
Google reported more than 1.3 million set-top boxes. TrendAI counted 1,472,554 infected devices between June 3 and October 1, 2026, and described its figure as a lower bound.
Does removing an app get rid of the backdoor?
Not necessarily. According to Google’s account, the backdoor was embedded in firmware and could reinstall itself from a protected partition after a reboot. The source material does not give a universal removal procedure.
Were certified Android TV boxes infected?
Google says some affected devices were Google-certified. It said the manufacturer used obfuscation to load malicious code after the first boot and that Google has since banned Videostrong from its certified-device program and tightened firmware checks.
What should owners do if they suspect their box is affected?
The source account recommends checking Play Protect certification, treating suspicious devices as untrusted, unplugging or replacing them, and keeping TV boxes on a separate guest network. It does not provide a confirmed list of affected models.
Source: ThorstenMeyerAI.com