🔍 Read the full analysis: Record CVEs To Crypto Heist: AI’s Place In Black October 2026 on ThorstenMeyerAI.com

Get smart everyday buys delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
TL;DR
A November 1 report by Thorsten Meyer says October 2026 set records for published CVEs and crypto losses, while CISA added 36 vulnerabilities to its Known Exploited Vulnerabilities catalog. The report attributes the largest crypto loss to a Binance theft the FBI linked to North Korea, but its figures do not establish that AI caused the CVE surge or the theft.
Meyer says he counted 17,060 new records in the National Vulnerability Database (NVD) in October, excluding rejected records. That is four times October 2025’s 4,273. From January through October, his NVD API count was 89,859, compared with 39,639 over the same period in 2025. The report notes that including rejected records would raise October 2026’s total to 17,481.
CISA’s Known Exploited Vulnerabilities (KEV) catalog added 36 entries in October, according to the analysis, compared with 31 in October 2025 and 17 in 2024. Its January-to-October count reached 282, already above the 245 additions recorded for all of 2025. These are catalog additions, not a count of every attack or every vulnerability exploited worldwide.
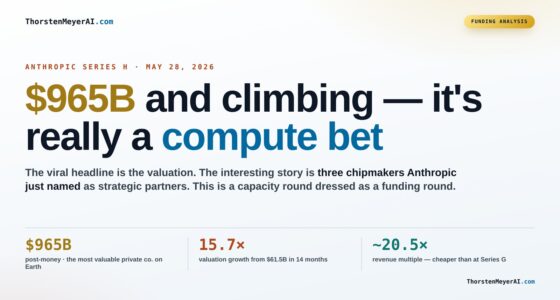
The report cites CertiK’s estimate of $3.47 billion in October crypto losses after frozen and returned funds, versus $68 million in October 2025. It says Binance accounted for 96.7% of the October total. The FBI attributed the Binance theft to North Korea’s “TraderTraitor” on October 31, according to Meyer; the supplied material does not include the FBI statement itself.
Infographic 01 · Three ledgers
Black October: three records, very different sizes
Disclosed flaws quadrupled. Exploited flaws rose, but far less. Crypto losses jumped because of one theft.
New CVE records
October 2026 · 4× October 2025
Added to CISA’s KEV list
October 2026 · known exploited flaws
Crypto losses after freezes
October 2026 · CertiK, adjusted
CVE: records by publication date, rejected records excluded. KEV: additions by date added. Crypto: CertiK “adjusted” = losses minus frozen or returned funds; other counters (Chainalysis, PeckShield) use different methods. Years compared January to October, because 2026 is not over.
Sources: NVD CVE API 2.0 (author query, 1 Nov 2026), CISA KEV catalog, version 2026.10.30, GTIG, 30 Sep 2026, CertiK Hack3D dashboard (adjusted losses), FBI, 31 Oct 2026, Microsoft October 2026 update file. Counts by Thorsten Meyer.
Powered by Thorsten Meyer AI
Disclosures Outpaced Known Exploitation
The difference between the two security counts matters for interpreting claims of a worsening threat. Published CVEs describe disclosed flaws; they do not prove that those flaws were attacked. KEV additions, by contrast, reflect CISA’s catalog of vulnerabilities for which it says there is reliable evidence of exploitation. In Meyer’s October figures, CVEs rose fourfold year over year while KEV additions rose from 31 to 36.
The report cites Google Threat Intelligence Group (GTIG) as estimating that only about one in 431 vulnerabilities disclosed in 2026 had been observed exploited. That estimate reinforces the need not to treat disclosure volume as a direct measure of attacks. At the same time, 282 KEV additions through October exceed the full-year 2025 count, suggesting defenders still face a growing set of documented exploited flaws.
The crypto-loss figure is a separate measure, and its concentration matters: Meyer says 96.7% of the monthly total came from the Binance incident. A single large theft can dominate a monthly aggregate, so the total alone does not show that crypto thefts broadly increased by the same amount or that AI was involved.
Products Worth Considering

Samsung 49-inch Odyssey OLED G9 (G91SD) Dual QHD Curved Gaming Monitor

Canon PIXMA PRO-200S Wireless Professional Inkjet Photo Printer

Apple MacBook Pro 14 2021 with M1 Max, 64GB RAM, 2TB SSD, Silver
As an affiliate, we earn on qualifying purchases.
How the Three Counts Differ
Meyer organizes the month around three measures: disclosed vulnerabilities, flaws added to CISA’s exploited catalog, and reported crypto losses. They have different methods and meanings. NVD counts public CVE records; KEV entries require evidence of active exploitation; crypto-loss totals track reported financial losses and can change when funds are frozen or returned.
The analysis says GTIG found exploitation rising roughly in step with disclosure over its January-to-August review, while its reported average of observed zero-days rose moderately, from eight to 11 per month. Meyer also describes at least 65 entries in Microsoft’s October security release as crediting an AI model or an AI vulnerability research firm, including a flaw already exploited in the wild. He says PHP2Shell, patched October 21, came from OpenAI’s Patch the Planet program, and Google’s Big Sleep found more actionable Chrome JavaScript-engine bugs than Google’s own fuzzer over six months.
These examples document AI-related vulnerability research and fixes, but they do not by themselves show that AI produced the month’s overall CVE increase. Meyer’s account also says the Binance theft began with a compromised laptop, rather than an AI-found vulnerability. That distinction is central to his assessment of AI’s role.
“The haystack grew much faster than the needles.”
— Thorsten Meyer, describing his interpretation
What the October Totals Cannot Show
The figures supplied do not establish that AI caused the record CVE count, the rise in KEV entries or the Binance theft. Meyer’s analysis says attackers can use AI to turn fixes into exploits within days and says the PHP2Shell embargo broke before release, but the supplied material gives limited detail to independently verify the timing or quantify AI’s role in exploitation.
The source also warns that CVE totals depend on counting method and assignment practices. It says automated assignment policies inflated some counts, citing about 5,000 Linux-kernel-related CVEs from January to August and no observed zero-day exploitation for those records, as reported by GTIG. The specific share of October’s total attributable to such practices is not provided. The supplied excerpt ends during its discussion of GTIG’s exploitation figures, so the full methodology and any additional caveats are unavailable here.
Details of the Binance incident beyond the FBI attribution, including the exact attack path, are not set out in the supplied material. Nor does the monthly comparison explain whether the October crypto-loss estimate is comparable across all incidents and reporting methods.
Follow-up on Catalogs and Attribution
The next useful checks are updated NVD and CISA catalog totals, further details from investigators about the Binance theft, and any subsequent revisions to the crypto-loss estimate. Those updates could change the month’s counts or clarify what is included in them.
For the AI question, more evidence would be needed on individual cases: when a flaw was found, when it was disclosed or patched, whether it was exploited, and whether AI materially contributed. Until then, the October numbers support a report of record disclosures and substantial reported losses, but not a conclusion that AI drove the month’s overall security outcomes.
Key Questions
What records did the report say October 2026 set?
Thorsten Meyer’s analysis counted 17,060 new NVD records in October, excluding rejected records, and reported $3.47 billion in crypto losses after frozen and returned funds. It also counted 36 October additions to CISA’s KEV catalog, but described those as a smaller increase than the CVE rise.
Did the CVE increase mean attacks increased fourfold?
No. The fourfold comparison is for published CVE records in October 2026 versus October 2025. CVEs record disclosed vulnerabilities; they are not a count of attacks. The report says CISA KEV additions rose from 31 to 36 over the same October comparison.
Who did the FBI blame for the Binance theft?
According to Meyer’s account, the FBI attributed the theft to North Korea’s “TraderTraitor” on October 31. The supplied source says the incident began with a compromised laptop, but does not provide further technical details or the FBI’s original statement.
Does the report prove AI caused the October records?
No. It describes AI-linked security research and patching, including Microsoft release credits and OpenAI’s Patch the Planet program, but does not establish that AI caused the CVE surge or Binance theft. Meyer presents his broader view as a thesis, not a measured finding.
Source: ThorstenMeyerAI.com